
Every day, thousands of small business owners click on emails that look completely legitimate, only to hand over sensitive information to cybercriminals without realizing it. If that sounds alarming, it should be. These attacks are not slowing down, and small businesses are increasingly becoming the primary targets.
So what exactly is phishing? The phishing definition, in plain terms, is a type of online scam where criminals disguise themselves as trustworthy sources to trick you into revealing passwords, financial details, or other sensitive data. It is one of the most common and damaging cyber threats facing small businesses today.
In this guide, you will get a clear, jargon-free breakdown of how phishing works, why your business is at risk, and what the most common attack types look like in the real world. More importantly, you will walk away with practical steps to protect yourself and your team. No technical background is required. Whether you have five employees or fifty, understanding this threat is the first and most important step toward keeping your business safe.
The One-Sentence Definition (and Why It Matters to Your Business)
Phishing is a criminal sending you a fake but convincing message designed to trick you into handing over access, money, or sensitive information. That single sentence captures everything that matters: it is deliberate, it is deceptive, and it targets you rather than your software.
This distinction is critical for every business owner to understand. Phishing is a con, not a hack. Attackers are not sitting in a dark room trying to crack your firewall or exploit a software flaw. They are crafting a believable email that looks like it came from your bank, your payroll platform, or even your own CEO, and then waiting for a trusted employee to do exactly what the message asks. Because the attack travels through normal business workflows and exploits human trust, traditional technical security controls alone cannot stop it. A firewall cannot block a decision a person makes voluntarily.
The numbers confirm how serious this threat is. According to the Verizon 2025 Data Breach Investigations Report, phishing is involved in 36% of all data breaches, making it the single most common entry point into organizations across every industry. IBM categorizes phishing squarely under social engineering, not malware, reinforcing that the vulnerability being exploited is human judgment, not a software patch that can simply be applied.
For small businesses in Des Moines, Ankeny, West Des Moines, and across central Iowa, the exposure is identical to that of a Fortune 500 company. Attackers do not filter their target lists by zip code or company size. The difference is that large enterprises typically have layered defenses, dedicated security teams, and formal response procedures already in place. Most small businesses do not.
This guide exists to close that knowledge gap. By the time you finish reading, you will have a clear, working understanding of phishing, the ability to recognize its warning signs, and practical steps you can take to protect your organization starting today.
How a Phishing Attack Actually Works
Understanding how a phishing attack unfolds in sequence makes it far easier to recognize one before it causes damage. Every phishing attack, regardless of how sophisticated it appears, follows the same four-stage structure: delivery, lure, action, and consequence.
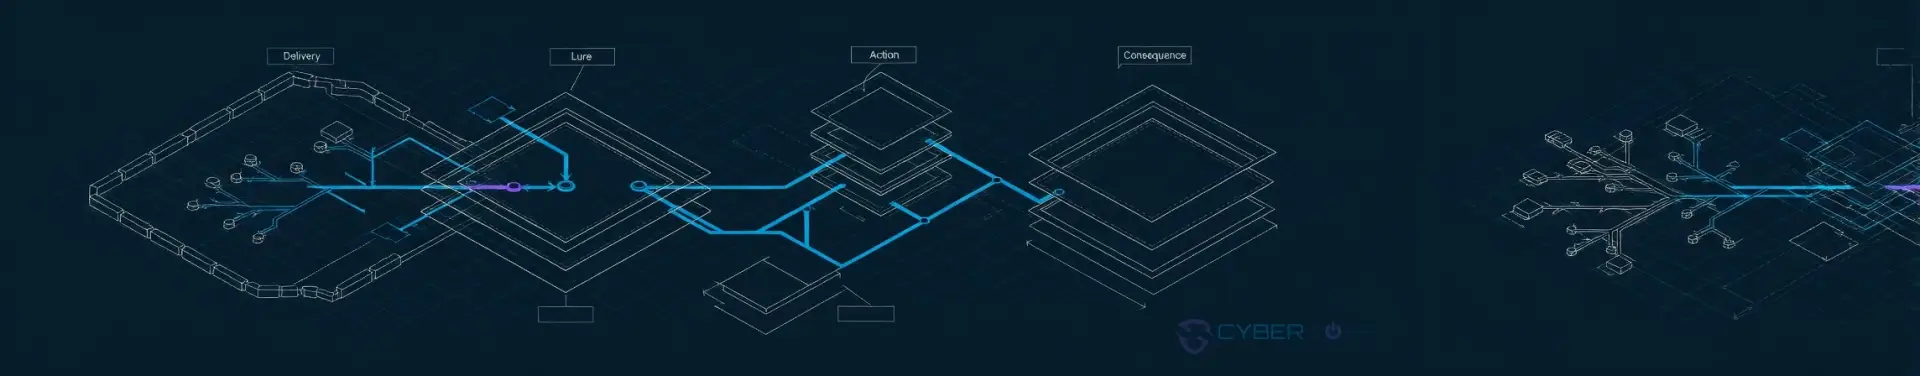
Delivery is where it begins. A carefully crafted email lands in your inbox, often bypassing spam filters because it originates from a domain that looks plausible or has not yet been flagged. No email filter catches everything, which means the first line of defense is always the person reading the message.
The lure is where attackers invest most of their effort. Consider a realistic scenario from right here in central Iowa: a behavioral health practice in the Des Moines metro receives what appears to be a routine password-reset notice from their electronic health records vendor. The email displays the vendor’s logo, matches the formatting of legitimate communications, and shows a familiar sender display name. Nothing looks out of place to a busy front-desk employee handling patient check-ins between messages.
The action happens faster than most people expect. According to the Verizon Data Breach Investigations Report 2025, the median time from email delivery to a user clicking a phishing link is just 21 seconds. Attackers are not counting on deliberate analysis; they are engineering reflexive behavior by combining a trusted identity with manufactured urgency. The employee clicks the link and lands on a login page that looks pixel-perfect, mirroring the real vendor portal down to the favicon. That page is frequently hosted on a domain registered only days earlier, meaning reputation-based security tools have no negative history to flag. Visual inspection is not a reliable defense.
The consequence is what makes the entire exercise worthwhile for the attacker. In most modern phishing campaigns targeting small businesses, the goal is not to install malware but to steal credentials. Logins to Microsoft 365, Google Workspace, and EHR portals are the primary targets, because small-business operations and sensitive data, including protected health information, now live almost entirely in cloud platforms. With a single set of stolen credentials, an attacker can access patient records, internal communications, financial data, and more, often going undetected for weeks.
The Phishing Family: Six Variants Every Business Owner Should Know
Phishing is not a single attack. It is a family of related tactics, each engineered to exploit a different communication channel or trust relationship. Understanding the distinctions between these variants is the first step toward recognizing them before they cause damage.
Email Phishing (Bulk Campaigns)
The most familiar variant is bulk email phishing: mass-blast campaigns sent simultaneously to millions of addresses with little to no personalization. The scale is staggering. Approximately 3.4 billion phishing emails are sent every day globally, and roughly 82.6% of them are now AI-generated, making them grammatically flawless and far harder to spot than the typo-riddled messages of a decade ago. Common lures include fake invoice notices, password-reset alerts, and urgent security warnings. These campaigns function as a numbers game: even a fraction-of-a-percent click rate across millions of recipients translates to thousands of compromised accounts.
Spear Phishing (Targeted Email)
Where bulk phishing casts a wide net, spear phishing uses a precision hook. These messages reference the recipient’s name, employer, job title, or recent activity to appear completely credible. This personalization is devastatingly effective: spear phishing initiates 91% of successful breaches, and AI now allows attackers to generate highly personalized messages at industrial scale. According to the latest phishing trend research, AI-powered spear phishing achieves a 54% click rate while costing attackers 95% less than hiring human experts. The Verizon DBIR 2025 found the median time from email delivery to a user clicking a malicious link is just 21 seconds, which means human recognition alone is rarely sufficient.
Business Email Compromise (BEC)
BEC is the most financially destructive phishing sub-type. Attackers impersonate an executive, CFO, or trusted vendor and instruct staff to redirect a wire transfer or divert a payment to a fraudulent account. The FBI’s Internet Crime Complaint Center recorded $2.77 billion in BEC losses across 21,442 complaints in 2024 alone. For law firms managing client escrow accounts and accounting practices handling trust funds or M&A transactions, BEC represents a direct and outsized financial and liability threat. A single successful attack can wipe out a client relationship, trigger a regulatory inquiry, and expose the firm to malpractice claims.
Vishing (Voice Phishing)
Vishing replaces the inbox with a phone call. Attackers impersonate IT support technicians, bank fraud departments, or government officials and use urgency to pressure staff into revealing one-time passcodes or account credentials. Vishing attacks surged 442% in the second half of 2024 per CrowdStrike’s 2025 report, a spike that reflects how attackers are pivoting to channels where employees have no formal verification protocol in place.
Smishing (SMS Phishing)
Smishing delivers malicious links via text message, typically impersonating delivery services, banks, or payroll platforms. A message reading “Your direct deposit failed, verify your account now” targets the same urgency response as an email lure but reaches employees on personal mobile devices that often lack enterprise security controls. Healthcare staff and field employees using personal phones for work communication face heightened exposure here.
Quishing (QR-Code Phishing)
Quishing is the newest variant in wide circulation and arguably the most technically deceptive. Attackers embed malicious QR codes in emails or physical materials, including printed flyers, conference badges, and lobby signage, that route users to credential-harvesting pages. The critical risk is that most email security filters scan URLs but cannot interpret image-encoded links, meaning quishing emails pass through standard defenses undetected. Employees who have been trained to hover over links before clicking have no equivalent instinct for QR codes, making awareness training that explicitly covers this variant an essential part of any current security program.
Why Small Businesses Are the Real Target
If your organization has fewer than 50 employees, you may have told yourself at some point that attackers have bigger fish to fry. That assumption is not just incorrect; it is actively dangerous. The threat landscape has changed in a fundamental way, and small businesses are no longer overlooked by default. They are, in many cases, the preferred target.
The reason comes down to economics. Phishing-as-a-Service (PhaaS) platforms have completely eliminated the technical skill barrier that once limited who could launch a sophisticated attack. Today, a threat actor with no programming knowledge can purchase a pre-built phishing kit that includes spoofed login pages, sending infrastructure, and ready-to-use target lists. That kit can be deployed against hundreds of small businesses simultaneously for minimal cost. According to current phishing attack research, PhaaS platforms now power between 60 and 90 percent of all credential thefts. A 12-person accounting firm in Ankeny and a regional law firm in West Des Moines are just as reachable as any Fortune 500 company, and far easier to compromise once reached.
Small businesses are attractive precisely because of what they lack. Their defenses are typically thinner, their staff receives less security training, and their incident response capabilities are slower than those of enterprise organizations. The human element was involved in 62 percent of confirmed data breaches in 2026, according to email security research from Adaptive Security. That human vulnerability is most exploitable where no structured awareness training exists, which describes the majority of small businesses. Attackers know this, and they factor it into target selection.
The stakes are especially high for the types of organizations common across the Des Moines metro. Independent healthcare practices, behavioral health providers, law firms, and financial services firms handle exactly what attackers want: protected health information, privileged client communications, and access to accounts that initiate wire transfers. These firms face targeted Business Email Compromise fraud and credential theft campaigns, not generic spam blasts. The FBI has documented BEC fraud activity across all 50 states, with $2.77 billion in reported losses from 21,442 complaints in 2024 alone.
The financial trajectory confirms the urgency. Global phishing losses are projected to reach $25 billion annually by 2026, and a disproportionate share of that figure falls on small and mid-sized organizations. Larger companies detect intrusions faster and contain damage more quickly because they have dedicated security staff and monitoring infrastructure in place. Organizations without those resources experience longer attacker dwell times, which translates directly into larger financial losses and more extensive data exposure. Being small does not make your organization invisible; it makes recovery harder if an attack succeeds.
Outdated Advice That No Longer Protects You
The most widely repeated advice in cybersecurity awareness training is now working against you. For years, employees were taught to spot phishing by looking for telltale signs: misspelled words, awkward grammar, generic greetings like “Dear Valued Customer.” That guidance made sense when attackers were manually composing mass-blast emails with limited English skills. It no longer reflects reality. According to research from Keepnet and VIPRE, 82.6% of phishing emails today are AI-generated, producing messages that are grammatically flawless, contextually appropriate, and indistinguishable in tone from legitimate business correspondence. Relying on a spell-checker instinct to protect your organization in 2025 is like installing a screen door to stop a hurricane.
The financial and operational data behind this shift is alarming. A 2024 Harvard Business Review study found that AI-powered spear phishing campaigns achieved a 54% click rate while costing attackers 95% less than campaigns run by human expert attackers. That combination of higher effectiveness and near-zero marginal cost has fundamentally changed who can launch a precision attack and against whom. Previously, targeted spear phishing required skilled social engineers doing manual research. Today, any low-level threat actor can generate thousands of hyper-personalized, contextually accurate messages in minutes. Spear phishing in 2026 research confirms that AI has removed content-based red flags entirely, making context and intent the only reliable detection signals remaining.
The volume problem is also accelerating. A 14x increase in AI-generated phishing attacks is projected for 2026, and attackers are no longer limited to email as a delivery channel. Emerging vectors include SVG file attachments and calendar invites designed specifically to bypass conventional email security filters. These novel formats exploit the fact that most filters are trained to evaluate message text, not embedded file structures or calendar metadata. Understanding how AI is transforming phishing attacks helps clarify why perimeter defenses alone are insufficient.
What to Watch for Instead
Since polished writing no longer signals safety, train yourself and your team to evaluate behavior and context, not grammar. The red flags that matter now include:
- Unexpected urgency: phrases like “act within 24 hours” or “your account will be suspended” are manufactured pressure designed to short-circuit careful thinking
- Out-of-workflow requests: a vendor emailing new wire transfer instructions, an HR notice requesting direct deposit changes through an unfamiliar link
- Mismatched context: an IT security alert for a software system you do not actually use, or an invoice from a vendor your organization has never worked with
- Any request involving credentials or payment: especially those directing you to click a link rather than log in through a known, bookmarked portal
Why Human Instinct Needs Technical Backup
Even well-trained employees cannot catch every AI-crafted message, particularly when the median time from email delivery to a user clicking a phishing link is just 21 seconds. Effective defense requires layered technical controls working alongside trained humans. Email authentication standards including SPF, DKIM, and DMARC verify that incoming messages actually originate from the domains they claim to represent, blocking a large category of spoofed sender attacks before they reach an inbox. Advanced email filtering adds behavioral analysis on top of that foundation. Simulated phishing training, delivered continuously rather than as a one-time annual session, conditions employees to recognize behavioral red flags through repeated practice. AI phishing detection research confirms that organizations combining technical controls with ongoing simulation-based training reduce phishing susceptibility to under 5%, compared to organizations relying on employee instinct alone.
Phishing Is a Compliance Issue, Not Just an IT Issue
Most small business owners think of phishing as an IT problem. A suspicious email arrives, the IT person handles it, and life moves on. That framing is dangerously incomplete. When a phishing attack succeeds, it does not simply create a technical incident; it creates a regulatory event with documented notification obligations, enforcement exposure, and financial consequences that fall on the business owner, not the IT vendor.
When a Single Click Becomes a HIPAA Breach
Consider a realistic scenario: a front-desk employee at a medical practice receives a convincing email appearing to come from Microsoft, clicks a link, and enters her Microsoft 365 credentials on a fake login page. Within hours, an attacker is reading emails inside that account, including messages that contain protected health information (PHI). Under the HIPAA Breach Notification Rule, that moment of unauthorized access constitutes a reportable breach. The practice must notify every affected patient in writing and submit a report to the Department of Health and Human Services within 60 days of discovery. If more than 500 Iowa residents are affected, the breach must also be reported to prominent local media. The regulatory clock starts at discovery, meaning delayed detection does not reduce liability; it compounds it.
Behavioral Health Practices Face a Layered Obligation
Behavioral health and substance use disorder practices carry additional exposure that general medical providers do not. A phishing-driven breach at a behavioral health office may simultaneously trigger HIPAA notification requirements and Iowa state law obligations under Iowa Code Chapter 715C, the state’s data breach notification statute, which governs the timing and scope of consumer notification for breaches of personally identifiable information. Mental health and substance use records often carry stricter confidentiality protections under both federal and state law, making notification requirements more demanding than those applied to standard medical records. For a small behavioral health practice, a single phishing incident can generate multiple overlapping compliance obligations at once.
Financial Firms and Law Firms: The FTC Safeguards Rule
Under the FTC Safeguards Rule (16 CFR Part 314, expanded requirements effective June 2023), financial services firms and law firms handling consumer financial data are required to maintain a written incident response plan. A phishing-driven credential theft that goes undetected and undocumented is not just a security failure; it is a compliance failure. The amended Rule also requires notification to the FTC within 30 days of discovering a breach affecting 500 or more customers. Firms without a documented incident response process, including logging, assessment, and reporting procedures, face enforcement exposure independent of whether customer data was ultimately misused.
PCI DSS and Payment Card Environments
Organizations that process credit or debit card payments operate under PCI DSS, which includes specific incident response requirements under Requirement 12.10 in version 4.0. A phishing attack that results in credential access to any system touching cardholder data must be logged, investigated, and documented in accordance with the standard. Failing to detect a phishing intrusion, or detecting it but failing to document the investigation properly, can jeopardize PCI compliance status and expose the business to fines from card brands and acquiring banks.
The Cost Calculation That Should Concern Every Owner
Peer-reviewed research on organizational phishing consistently finds that most organizations concentrate resources on detection and awareness while underinvesting in the response and mitigation layer, which is precisely where compliance consequences accumulate. For small Iowa firms in regulated industries, the average cost of breach notification, including legal fees, notification letters, credit monitoring offers, and regulatory response, routinely exceeds the annual cost of the preventive controls that would have stopped the attack entirely. Phishing is not an IT department problem. It is an ownership-level business risk, and treating it as anything less is the decision most likely to result in a headline no small business can afford.
A Layered Defense Built for a 10-Person Office
Knowing what phishing is and knowing how to stop it are two very different things. The good news for a 10-person office is that effective protection does not require an enterprise IT department. It requires the right layers, applied in the right sequence, each one compensating for gaps in the others.
Layer 1: Email Security Filtering
The first layer intercepts threats before any employee ever sees them. Advanced email security tools authenticate sending domains using three standards: SPF (Sender Policy Framework), DKIM (DomainKeys Identified Mail), and DMARC (Domain-based Message Authentication, Reporting, and Conformance). Together, these protocols verify that an incoming message actually originated from the domain it claims to represent. Beyond authentication, modern email filters scan embedded links and attachments in real time, blocking malicious content before it reaches the inbox. This layer alone stops the overwhelming majority of commodity phishing attempts. For a small office without dedicated IT staff, this is non-negotiable infrastructure, not an optional upgrade.
Layer 2: Simulated Phishing Training
Technology filters cannot catch everything, and some attacks are specifically engineered to bypass them. That is where your people become either a vulnerability or a genuine defensive asset. Without structured training, roughly one in three employees will click a phishing link. Security awareness training combined with regular simulated phishing exercises, where staff receive realistic but harmless fake phishing emails and receive immediate feedback on their responses, reduces that susceptibility rate to under 5%. Annual checkbox-style training does not achieve this outcome; the improvement comes from ongoing, simulation-based programs that build and reinforce recognition skills over time. Simulated phishing is a core component of CyberCore360’s managed service offering precisely because trained employees compress attacker dwell time by recognizing and reporting threats faster.
Layer 3: Multi-Factor Authentication and Identity Controls
When credentials are stolen despite the first two layers, MFA serves as the critical failsafe. Multi-factor authentication requires a second verification step beyond a password, meaning a stolen login alone is not enough to access your Microsoft 365 or cloud applications. However, standard push-notification MFA is increasingly targeted by a technique called MFA fatigue, where attackers send repeated approval requests until a frustrated or inattentive user taps “approve” by mistake. Pairing MFA with employee awareness of this specific tactic is essential. Where possible, organizations should also move toward phishing-resistant MFA methods such as hardware security keys or passkeys, which cannot be intercepted or socially engineered the way push notifications can.
Layer 4: 24/7 Monitoring and Rapid Response
The Verizon DBIR 2025 data point that employees click phishing links within a median of 21 seconds carries a critical implication: the window between a credential being entered on a spoofed login page and an attacker accessing your systems is measured in minutes, not hours. Continuous monitoring that detects anomalous login behavior, such as an account signing in from an unfamiliar location or at an unusual hour, and triggers an immediate response is what closes that window. For a 10-person office, this level of coverage is not a luxury reserved for larger organizations. It is the difference between containing an incident quickly and discovering a breach weeks later.
Layer 5: Backup and Recovery
Even a well-defended organization will occasionally face a successful compromise. Phishing-driven breaches frequently lead to ransomware deployment or deliberate data deletion, both of which can bring operations to a halt. Verified, regularly tested backups, including cloud-to-cloud backups for SaaS environments, ensure that your practice or firm can recover its data and resume operations without paying a ransom or permanently losing client records. The emphasis on “tested” matters here; a backup that has never been restored is an untested assumption, not a recovery plan. This final layer is what transforms a potentially catastrophic incident into a recoverable one.
No single layer is sufficient on its own. Filters miss targeted attacks. Training reduces but does not eliminate human error. MFA can be bypassed by determined attackers. Monitoring means nothing without rapid response. And even the best prevention leaves a residual risk that only recovery capabilities can address. Together, these five layers create the kind of defense that gives a small organization a realistic chance of stopping most attacks and surviving the ones that get through.
What to Do If Someone on Your Team Clicks a Phishing Link
Even the most well-trained employee can click a wrong link on a stressful afternoon. When that happens, the response taken in the next few minutes determines whether the incident becomes a contained near-miss or a reportable data breach. Follow these five steps without delay.
Step 1: Do Not Panic, and Do Not Wait
The single most damaging thing an employee can do after clicking a phishing link is stay quiet and hope nothing happened. According to the Verizon 2025 Data Breach Investigations Report, the median time from email delivery to a user clicking a phishing link is just 21 seconds, but the median time to report the click is 28 minutes. That gap is exactly the window attackers exploit to use stolen credentials before anyone knows to look. Reporting immediately, even if the employee is embarrassed or uncertain whether anything bad actually occurred, converts a potential breach into a manageable containment event. Organizations should establish a blame-free reporting culture so that employees never hesitate out of fear of punishment. A fast, honest report is always the right move.
Step 2: Isolate the Affected Device
As soon as the click is reported, disconnect the device from the network immediately. Unplug the ethernet cable or disable Wi-Fi before doing anything else on that machine. This step matters because many phishing pages deliver malware silently in the background alongside the credential-harvesting form. Isolating the device cuts off any malware’s ability to communicate with attacker-controlled servers and prevents it from spreading laterally to other systems on the network. Do not turn the device off, which can destroy forensic evidence; simply remove it from network access and leave it for your IT provider to examine.
Step 3: Report to Your IT Provider or Security Team
Contact your managed IT or security provider through your designated incident reporting channel right away, and do not delete the original phishing email. Preserving the message, including the full headers and the link itself, helps your security team identify other employees who may have received the same campaign and block it before additional clicks occur. A qualified managed security provider can determine whether credentials were actually used, which data or systems may have been accessed, and whether the incident triggers breach notification obligations under HIPAA, the FTC Safeguards Rule, or PCI DSS. Do not attempt to investigate independently; the assessment requires security tooling and log access that your provider controls.
Step 4: Reset All Potentially Compromised Credentials
Password resets alone are not sufficient. Perform all credential resets from a separate, known-clean device, not the one that was compromised. Change the password for the affected account and every other account that shares the same password, prioritizing email, cloud applications, financial accounts, and any administrator accounts. Beyond passwords, revoke all active sessions in Microsoft 365 or Google Workspace so that any session tokens an attacker may have captured are immediately invalidated. Also audit connected application permissions, because attackers frequently grant themselves OAuth access to cloud accounts that survives a password change entirely.
Step 5: Document Everything for Compliance Purposes
Regulated industries face a hard requirement to document phishing incidents, not just remediate them. Under HIPAA, the FTC Safeguards Rule, and PCI DSS, organizations must maintain records of the incident timeline, the nature of the phishing email, the specific actions taken by the affected employee, the systems that were potentially accessed, and every remediation step completed. This documentation serves two purposes. First, it satisfies regulatory incident response obligations and supports any required breach notification analysis. Second, it strengthens your position with a cyber insurance carrier if a claim becomes necessary. Build this log in real time as the response unfolds, because reconstructing a timeline hours or days later produces incomplete records that regulators and insurers will scrutinize.
The Bottom Line on Phishing
Phishing remains the most common entry point for data breaches because it does not need to defeat your firewall or crack your passwords. It only needs to fool one person for roughly 21 seconds. In an era of AI-generated campaigns and Phishing-as-a-Service kits, the assumption that your organization is too small or too obscure to be worth targeting is simply no longer accurate.
The defense is achievable, even without internal IT staff. A combination of filtered email security, consistent awareness training, enforced multi-factor authentication, and a documented incident response plan can reduce both the probability and the damage of a successful attack. Security awareness training alone can cut phishing susceptibility to under 5 percent.
For small businesses in Iowa’s regulated industries, the consequences of a successful phishing attack extend well beyond a disrupted workday. HIPAA penalties, FTC Safeguards Rule violations, and Iowa’s breach notification requirements make phishing prevention a financial and legal priority that belongs at the ownership level, not the help-desk level.
If you are unsure whether your current IT setup would catch a phishing attempt before damage is done, that question deserves a direct answer. CyberCore Technologies builds security into every service plan rather than treating it as a billable add-on. Contact us to talk through where your current setup stands.
Conclusion
Phishing is one of the most common threats your small business faces, but it is also one of the most preventable. Here is what to remember: phishing attacks disguise themselves as trusted sources to steal sensitive information; small businesses are high-value targets precisely because they often lack formal security measures; and recognizing the warning signs, like suspicious links, urgent requests, and mismatched email addresses, can stop an attack before it causes damage.
The good news is that you do not need a large IT budget or a technical background to protect your business. Awareness is your most powerful tool.
Start today. Share what you have learned with your team, review your email security settings, and create a simple policy for handling suspicious messages. Small steps taken now can prevent costly consequences later.