

A lot of cyberattacks on small businesses start the same way. Someone opens a message that looks completely normal, clicks a link or answers a request, and hands over something an attacker wanted. That’s phishing, and it’s one of the most common ways criminals get into small organizations.
This guide explains what phishing means in plain terms, how an attack actually works, the forms it takes, and the warning signs your team can learn to recognize. No technical background required.
What Phishing Means
Phishing is a scam where a criminal pretends to be someone you trust so you’ll do something that helps them. That might mean entering your password on a fake login page, opening an attachment that installs malicious software, or sending a payment to the wrong account.
The key idea is impersonation. The attacker doesn’t need to break through your firewall. They only need one person to believe the message is real and act on it. The word itself is a play on “fishing”: the attacker casts out a lure and waits for someone to bite.
How a Phishing Attack Works
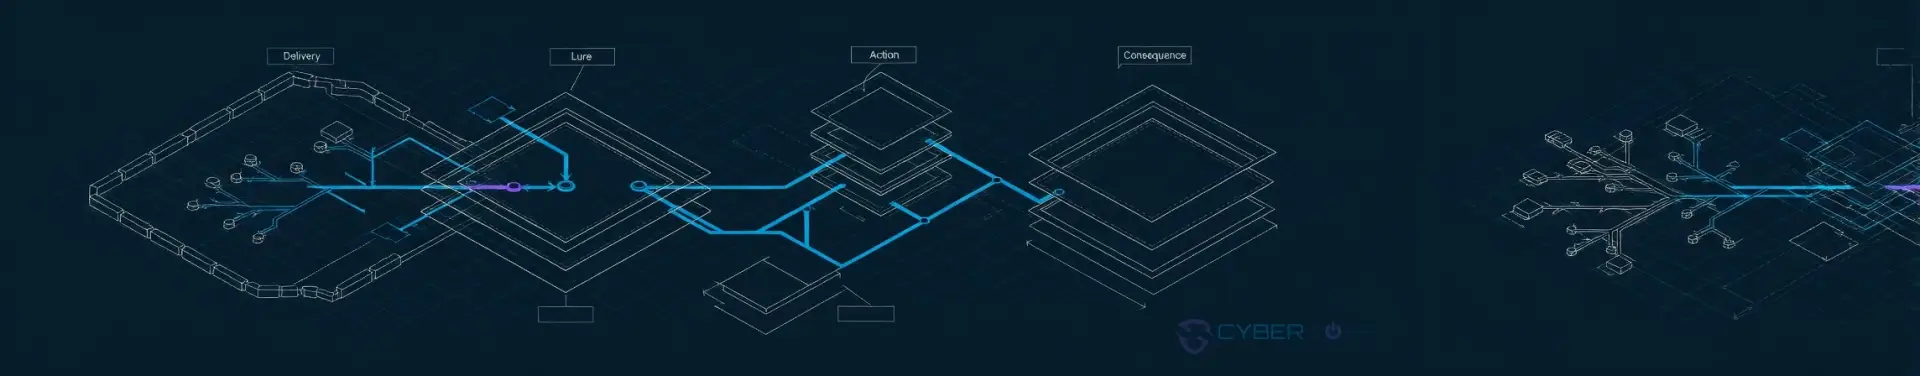
Most phishing attempts follow the same basic pattern.
The lure. A message arrives that appears to come from a familiar source: your email provider, a bank, a vendor, a delivery service, or even a coworker. It usually creates a reason to act quickly, such as an expiring password, a failed payment, or an urgent request from a manager.
The action. The message asks you to do one thing: click a link, open a file, reply with information, or approve a transaction. Links often lead to a login page that looks identical to the real one.
The payoff. Once you act, the attacker gets what they came for. Stolen login credentials are the most common prize, because a working email login can open the door to client files, financial records, and more.
Here’s a realistic example. An office manager at a small practice gets an email that looks like it came from the company’s email provider, warning that her password expires today. She clicks the link, enters her username and password on a convincing page, and moves on with her day. The attacker now has access to her mailbox and everything in it.
Common Types of Phishing
Phishing isn’t limited to email. These are the forms your team is most likely to encounter.
Email Phishing
Mass emails sent to thousands of people at once, imitating well-known companies or common business notices like invoices and shipping updates. They rely on volume: if even a few people click, the attacker wins.
Spear Phishing and Whaling
Spear phishing is targeted. The attacker researches a specific person or business using public information, such as a company website or social media profiles, and writes a message that references real names, vendors, or projects. Whaling is the same approach aimed at owners, partners, and others with authority to approve payments.
Business Email Compromise
In business email compromise, an attacker poses as an executive, a vendor, or a client and asks someone to wire money, change payment details, or send sensitive documents. It’s one of the most expensive forms of fraud: the FBI’s Internet Crime Complaint Center reported about $2.77 billion in business email compromise losses in 2024.
Smishing and Vishing
Smishing uses text messages, often posing as a bank, delivery service, or payroll system. Vishing uses phone calls, where a caller pretends to be tech support, a bank, or a government agency and pressures you to share a code or password.
QR Code Phishing
Some attacks hide a malicious link inside a QR code in an email or on a printed flyer. Because you can’t see the destination before scanning, it’s easy to land on a fake login page without realizing it.
Why Small Businesses Get Targeted
Attackers don’t pick targets based on size. Automated tools let them send convincing messages to thousands of organizations at once, and small businesses often have fewer safeguards in place. There may be no one whose job is to watch for suspicious activity, and staff may never have been shown what to look for.
Many small organizations also hold exactly the kind of information criminals want: patient records, client financial files, tax documents, and access to accounts that move money. According to the FBI’s 2024 Internet Crime Report, phishing and spoofing were the most frequently reported type of complaint that year.
How to Spot a Phishing Attempt
The old advice was to watch for typos and awkward grammar. That’s no longer reliable. Many phishing messages are now well written and professionally formatted. Instead, pay attention to context and behavior:
- Unexpected urgency. Deadlines, threats of account suspension, or pressure to act before you can think.
- Requests outside the normal routine. New payment instructions, a request for gift cards, or a document you weren’t expecting.
- A sender address that doesn’t quite match. The display name may look right while the actual email address is slightly off.
- Links that lead to login pages. When in doubt, go to the website directly instead of clicking the link.
- Requests involving money or credentials. Verify these by calling the person at a number you already know, not one listed in the message.
What to Do If You Clicked
Mistakes happen, and fast reporting makes a big difference. If you think you clicked something you shouldn’t have:
- Stop and don’t click anything else.
- Disconnect the device from Wi-Fi or unplug the network cable, but leave it powered on.
- Don’t delete the suspicious message, since your IT provider will want to examine it.
- Report it right away to your IT provider and your manager.
- Change your password from a different, trusted device if your IT provider recommends it.
A workplace where people feel comfortable reporting mistakes is far safer than one where they stay quiet and hope for the best.
Building Better Habits Across Your Team
Phishing works because it targets people, so protection has to include people too. Filtering suspicious email, requiring multi-factor authentication, and giving staff regular, practical training all work together to reduce the chances that one click turns into a serious problem.
CyberCore Technologies helps small businesses across Des Moines and central Iowa put those layers in place, including security awareness training with simulated phishing so your team gets comfortable spotting real threats. If you’d like to talk through where your organization stands, we’re happy to have that conversation whenever it’s useful for you.